Innspark
Threat Intelligence
An extensive collection of indicators with global impact, spanning threats that could compromise data and assets. Innspark uses them to strengthen detection and response.
Innspark
Threat Intelligence
An extensive collection of indicators with global impact, spanning threats that could compromise data and assets. Innspark uses them to strengthen detection and response.
Why Innspark Threat Intelligence?
Global, adaptable, and
actionable intelligence
Enhanced Threat Visibility
The global data pool delivers indicators on modern ransomware, state-sponsored espionage campaigns, and APTs.
Enhanced Threat Visibility
The global data pool delivers indicators on modern ransomware, state-sponsored espionage campaigns, and APTs.
Enhanced Threat Visibility
The global data pool delivers indicators on modern ransomware, state-sponsored espionage campaigns, and APTs.
Faster Detections & Response
Flexible security stack integration and automated event enrichment enable faster threat detection, decision-making, and response.
Faster Detections & Response
Flexible security stack integration and automated event enrichment enable faster threat detection, decision-making, and response.
Faster Detections & Response
Flexible security stack integration and automated event enrichment enable faster threat detection, decision-making, and response.
Defense Against Potential Threats
Industry-specific signatures of threat actors and campaigns reveal imminent risks and support advance defense preparation.
Defense Against Potential Threats
Industry-specific signatures of threat actors and campaigns reveal imminent risks and support advance defense preparation.
Defense Against Potential Threats
Industry-specific signatures of threat actors and campaigns reveal imminent risks and support advance defense preparation.
How does it work?


Accelerate Investigations with Actionable Threat Intelligence
Enrich incidents with curated indicators to identify hidden threats and fuel focused responses.
Accelerate Investigations with Actionable Threat Intelligence
Enrich incidents with curated indicators to identify hidden threats and fuel focused responses.
Accelerate Investigations with Actionable Threat Intelligence
Enrich incidents with curated indicators to identify hidden threats and fuel focused responses.
Accelerate Investigations with Actionable Threat Intelligence
Enrich incidents with curated indicators to identify hidden threats and fuel focused responses.
Actionable Insights, Continuously Curated
A team of researchers, malware analysts, and threat hunters curates indicators to identify hidden threats, continuously updated across security layers.

Reducing Alert Fatigue
Indicators enrich each incident with malware tags, threat actor identities, campaign details, and location, helping teams identify critical incidents quickly.

Accelerating Investigations & Responses
Enhanced context helps security teams anticipate incident impact, quickly identify critical ones, and initiate focused investigations and responses.

Bringing Intelligence Across Infrastructure
Innspark Threat Intelligence eliminates silos across security systems, integrating with other solutions to deliver threat visibility and faster incident handling.
Why Innspark Threat Intelligence?
Global, adaptable, and actionable intelligence
Enhanced Threat Visibility
The global data pool delivers indicators on modern ransomware, state-sponsored espionage campaigns, APTs, and more.
Faster detections & responses
Flexible security stack integration and automated event enrichment enable faster threat detections, decision-making, and responses.
Defend against potential threats
Get industry-specific signatures of threat actors and campaigns to know your imminent risks and prepare defenses in advance.
Features
Key Operational Capabilities of Innspark Threat Intelligence
Extensive Data Pool
Maintains global repositories of file hashes, IP addresses, URLs, domains, and JA3 fingerprints for threat intelligence.
Universal threat coverage
Delivers indicators covering malware, threat actors, OT, IoT, and enterprise assets for broader detection coverage.
Flexible Integrations
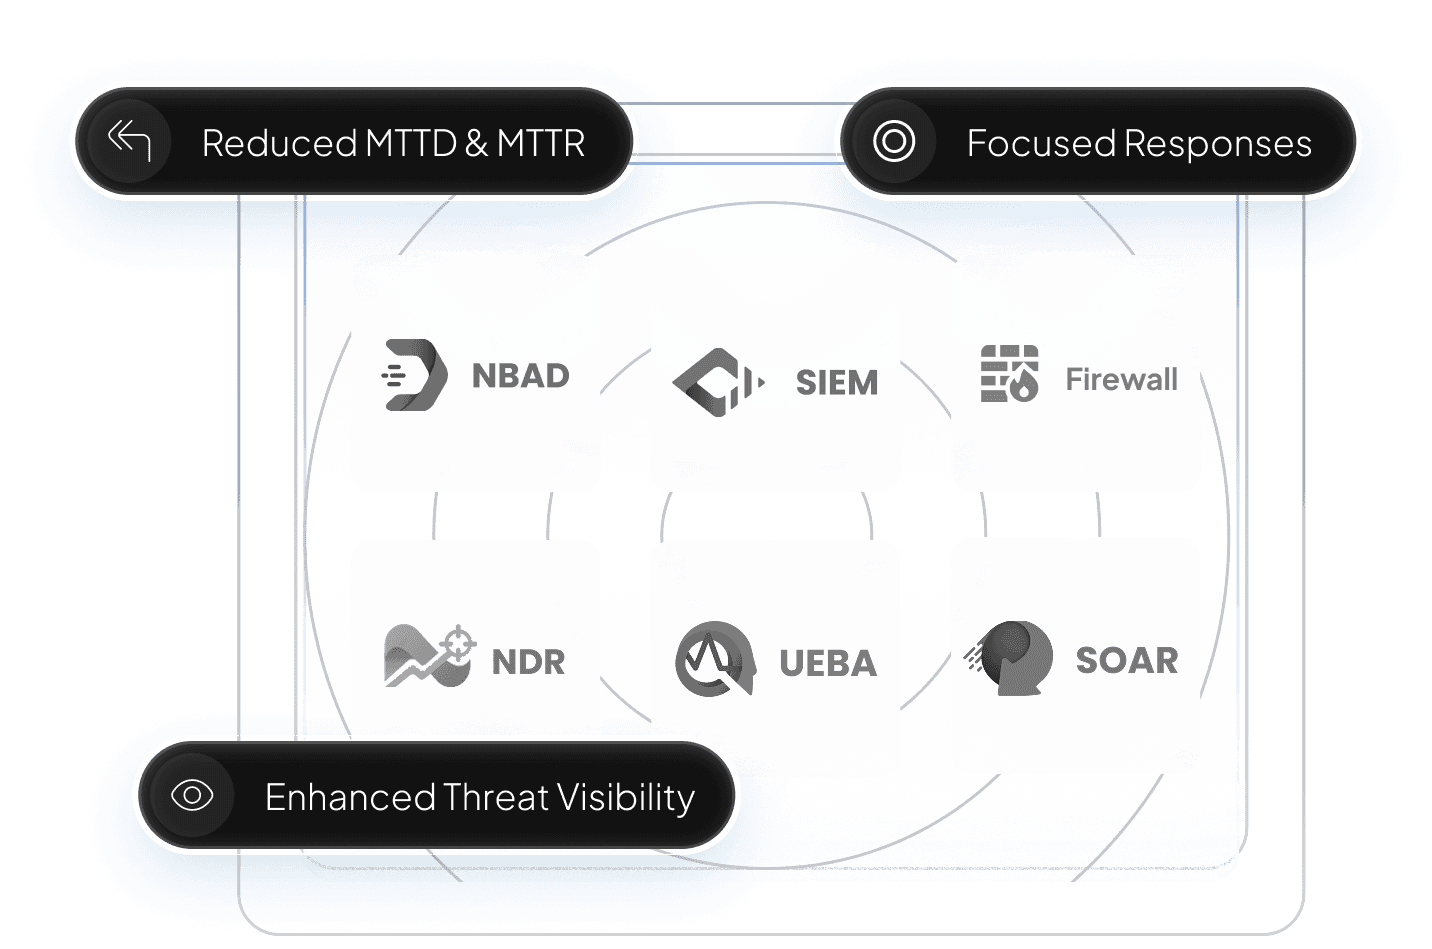
Integrates with SIEM, NDR, NBAD, SOAR, and security platforms to strengthen detection, investigation, and response.
Broader Threat Visibility
Continuously updates threat indicators to detect ransomware, spear phishing, DDoS attacks, APTs, and emerging cyber threats.
Sector-Focused Insights
Provides industry-specific indicators covering manufacturing, healthcare, financial services, energy, and other critical infrastructure sectors.
Actionable Native Insights
Delivers curated indicators protecting government and enterprise infrastructure against cyber espionage and operational sabotage.
Related solutions
Other cybersecurity solutions from Innspark
Other cybersecurity solutions from Innspark
Other cybersecurity solutions from Innspark
Explore Innspark's full portfolio of cybersecurity solutions, built to defend against threats and ensure business continuity.
Explore Innspark's full portfolio of cybersecurity solutions, built to defend against threats and ensure business continuity.
Explore Innspark's full portfolio of cybersecurity solutions, built to defend against threats and ensure business continuity.


FAQs
Get the Answers You Need
FAQs
Get the Answers You Need
What is threat intelligence data?
Why use threat intelligence in cybersecurity?
How does Innspak Threat Intelligence feeds improve my security?
Does Innspark provide threat intelligence embedded by default, or is separate subscription required?

Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence
Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence

Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence
Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence
Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence
Ready to see Innspark Threat Intelligence in action?
Schedule a personalized demo to explore Innspark Threat Intelligence
Features
Key Operational Capabilities of Innspark Threat Intelligence
Extensive Data Pool
Maintains global repositories of file hashes, IP addresses, URLs, domains, and JA3 fingerprints for threat intelligence.
Universal threat coverage
Delivers indicators covering malware, threat actors, OT, IoT, and enterprise assets for broader detection coverage.
Flexible Integrations
Integrates with SIEM, NDR, NBAD, SOAR, and security platforms to strengthen detection, investigation, and response.
Broader Threat Visibility
Continuously updates threat indicators to detect ransomware, spear phishing, DDoS attacks, APTs, and emerging cyber threats.
Sector-Focused Insights
Provides industry-specific indicators covering manufacturing, healthcare, financial services, energy, and other critical infrastructure sectors.
Actionable Native Insights
Delivers curated indicators protecting government and enterprise infrastructure against cyber espionage, sabotage, and advanced persistent threats.
Extensive Data Pool
Maintains global repositories of file hashes, IP addresses, URLs, domains, and JA3 fingerprints for threat intelligence.
Universal threat coverage
Delivers indicators covering malware, threat actors, OT, IoT, and enterprise assets for broader detection coverage.
Flexible Integrations
Integrates with SIEM, NDR, NBAD, SOAR, and security platforms to strengthen detection, investigation, and response.
Broader Threat Visibility
Continuously updates threat indicators to detect ransomware, spear phishing, DDoS attacks, APTs, and emerging cyber threats.
Sector-Focused Insights
Provides industry-specific indicators covering manufacturing, healthcare, financial services, energy, and other critical infrastructure sectors.
Actionable Native Insights
Delivers curated indicators protecting government and enterprise infrastructure against cyber espionage and operational sabotage.
How does it work?
Cut the Noise to Detect Faster & Respond Smarter